> For the complete documentation index, see [llms.txt](https://docs.threatdefence.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.threatdefence.com/platform-management/platform-components/analyst-console.md).
# Analyst Console
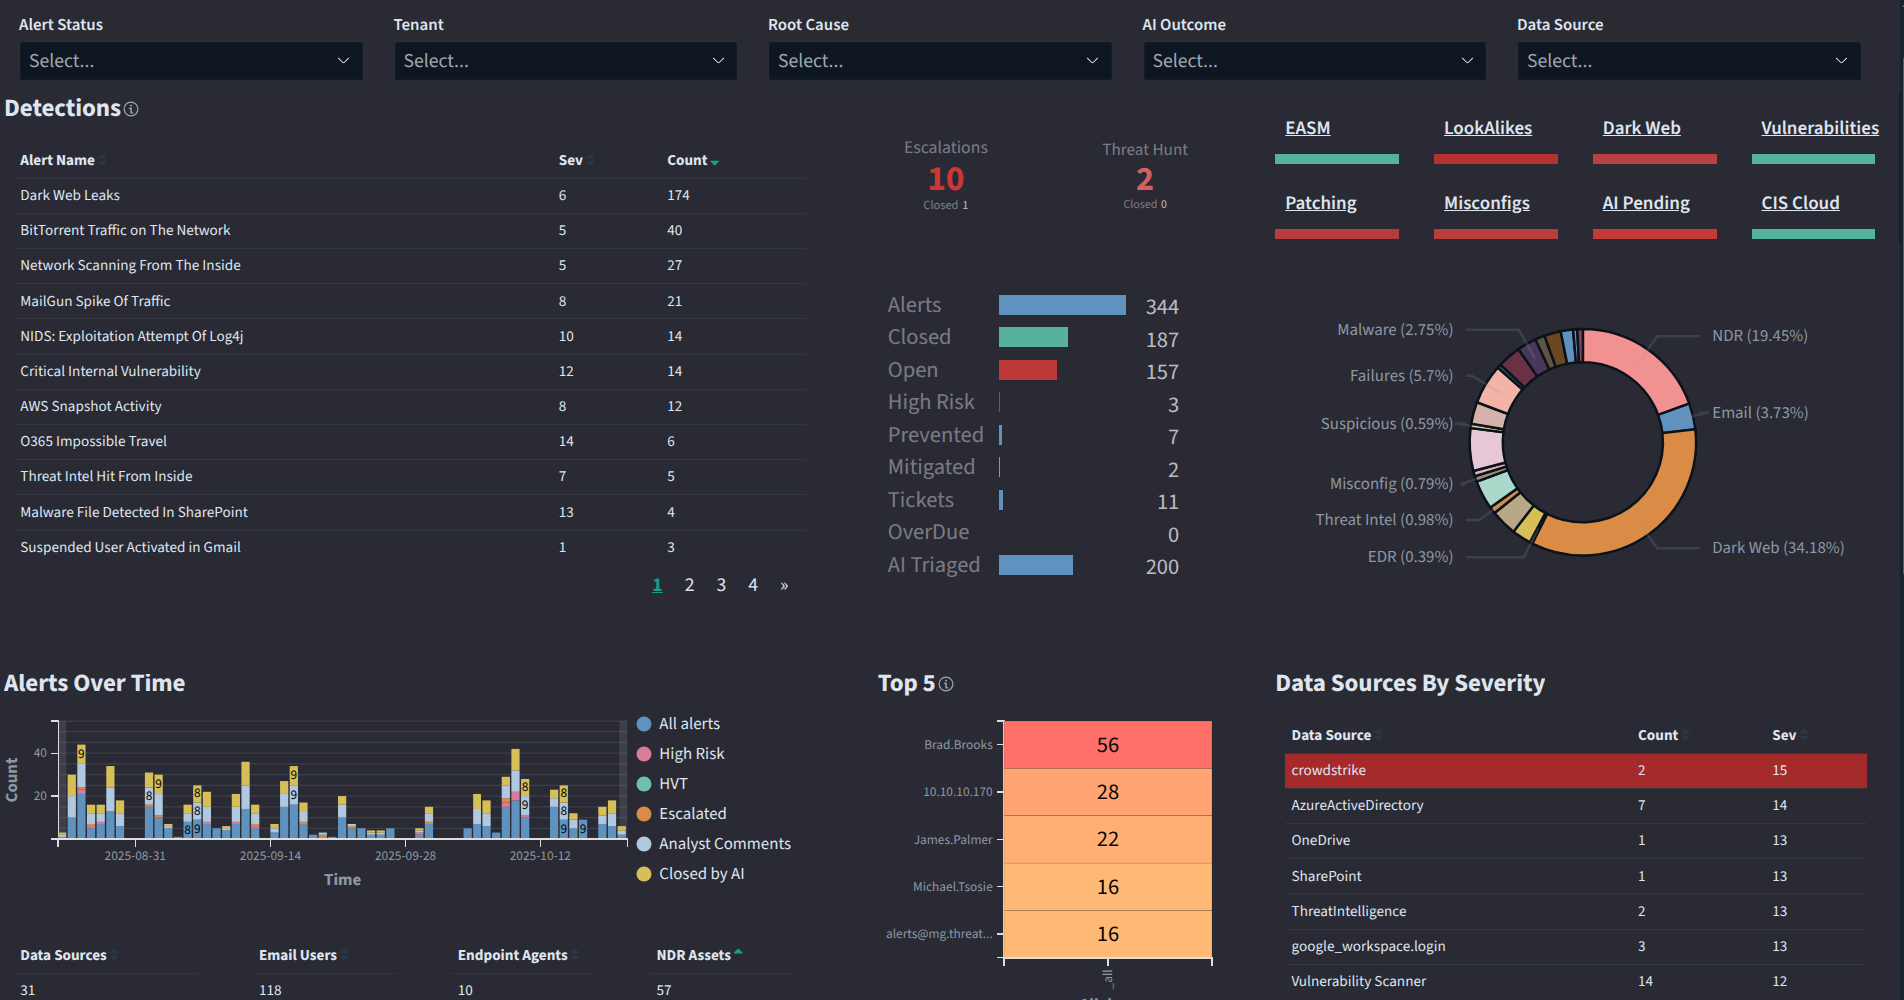
The Analyst Console is the main SIEM interface available to all eligible subscriptions. Tailored for security analysts, threat hunters, and incident responders, It provides access to your entire array of security event data and features a variety of dashboards and visualizations.
To access the console, navigate to [https://console.threatdefence.io](https://console.threatdefence.io/) and log in with your email and password.
Here are some examples of the information available via the Analyst Console:
* **Real-Time Threat Monitoring**: Observe live data streams of security events across your network, enabling immediate identification and investigation of suspicious activities.
* **Incident Management**: Track and manage security alerts and incidents from detection through resolution. This includes the ability to assign incidents, document response actions, and close incidents upon resolution.
* **Advanced Analytics**: Utilize sophisticated analytics tools to dissect and analyze security events. This can help identify trends, patterns, and anomalies within your security data, facilitating proactive threat hunting.
* **Dashboards**: Access dashboards that provide a detailed insights into your security events and posture. These dashboards can be tailored to highlight key metrics and data points relevant to your specific security concerns.
* **Search and Investigation Tools**: Employ powerful search capabilities and investigation tools to delve into historical security data. This enabled in-depth analysis of historical events and helps uncover the root cause of security breaches.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.threatdefence.com/platform-management/platform-components/analyst-console.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.